✓ ISO 9001 certified
✓ on the market since 2003 ✓ from Berlin, active worldwideThe occasion
Most audits begin with one of these three situations:
Hardly anyone orders a data protection audit out of pure interest. There is almost always a specific trigger – and that determines what we look at first.
Someone demands proof
A large customer, an investor, or the parent company wants to see that your data protection system works. They have documents, but nothing that they can present to you.
Data protection grew organically rather than by design
The list of processing activities dates back to the introduction phase; since then, new tools, new service providers, and AI applications have been added. No one knows what is still true.
Something has happened
A data breach, a complaint, or a request from the supervisory authority. Now it must be clear quickly and reliably where the gaps are and which ones need to be closed first.
The result
What you get at the end
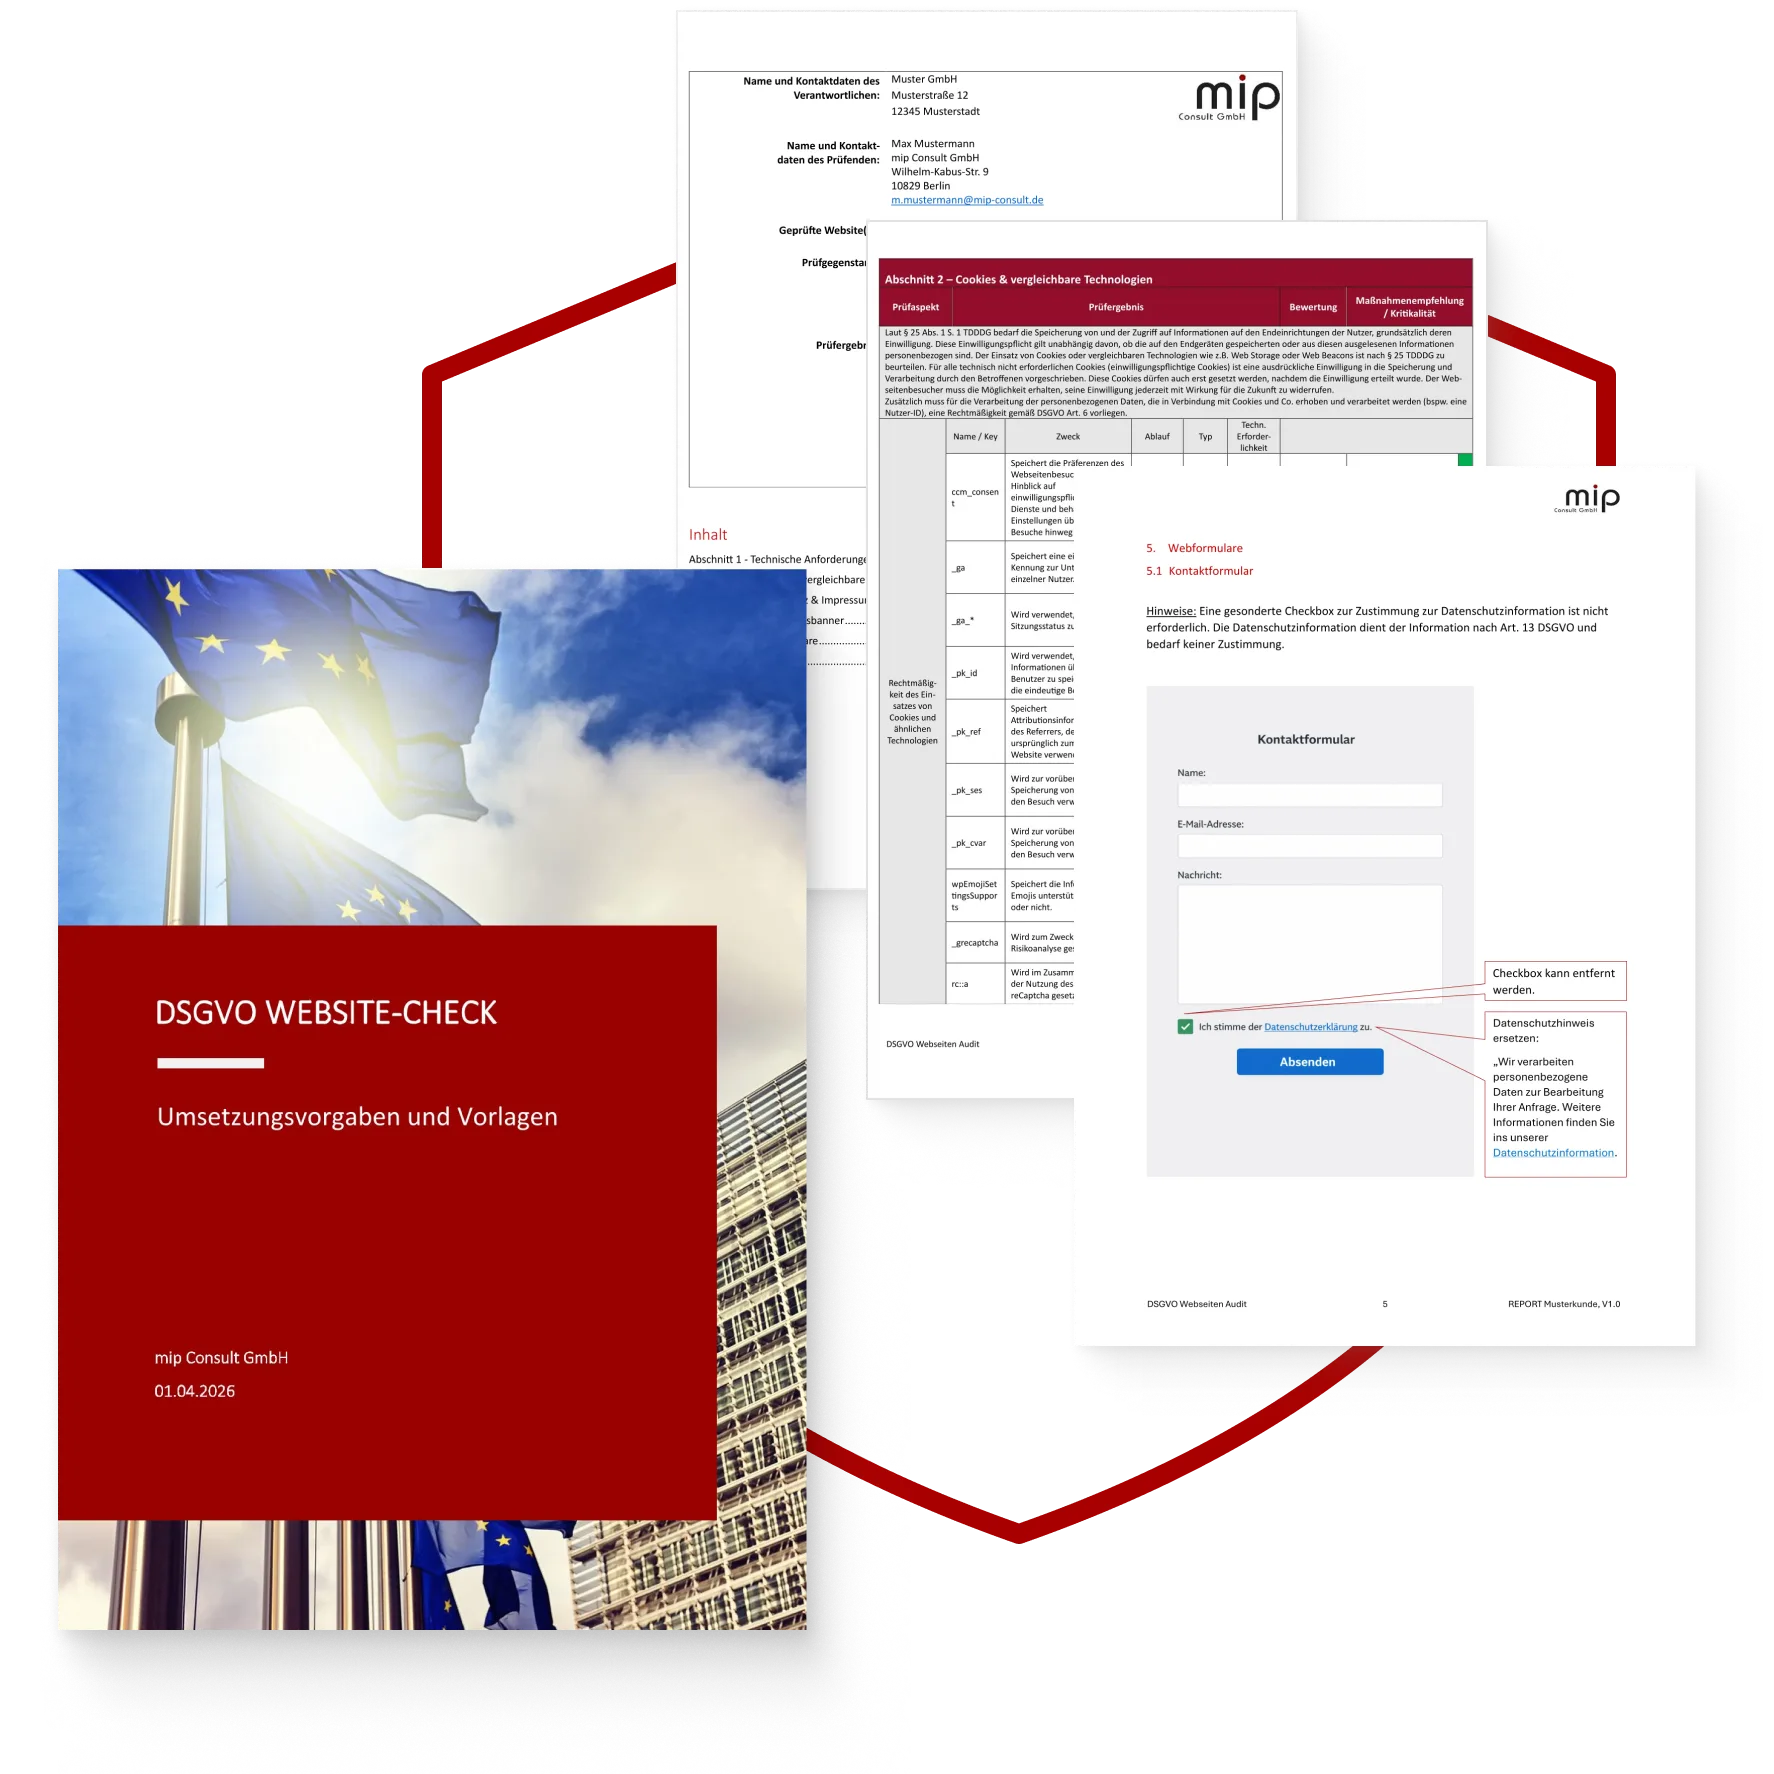
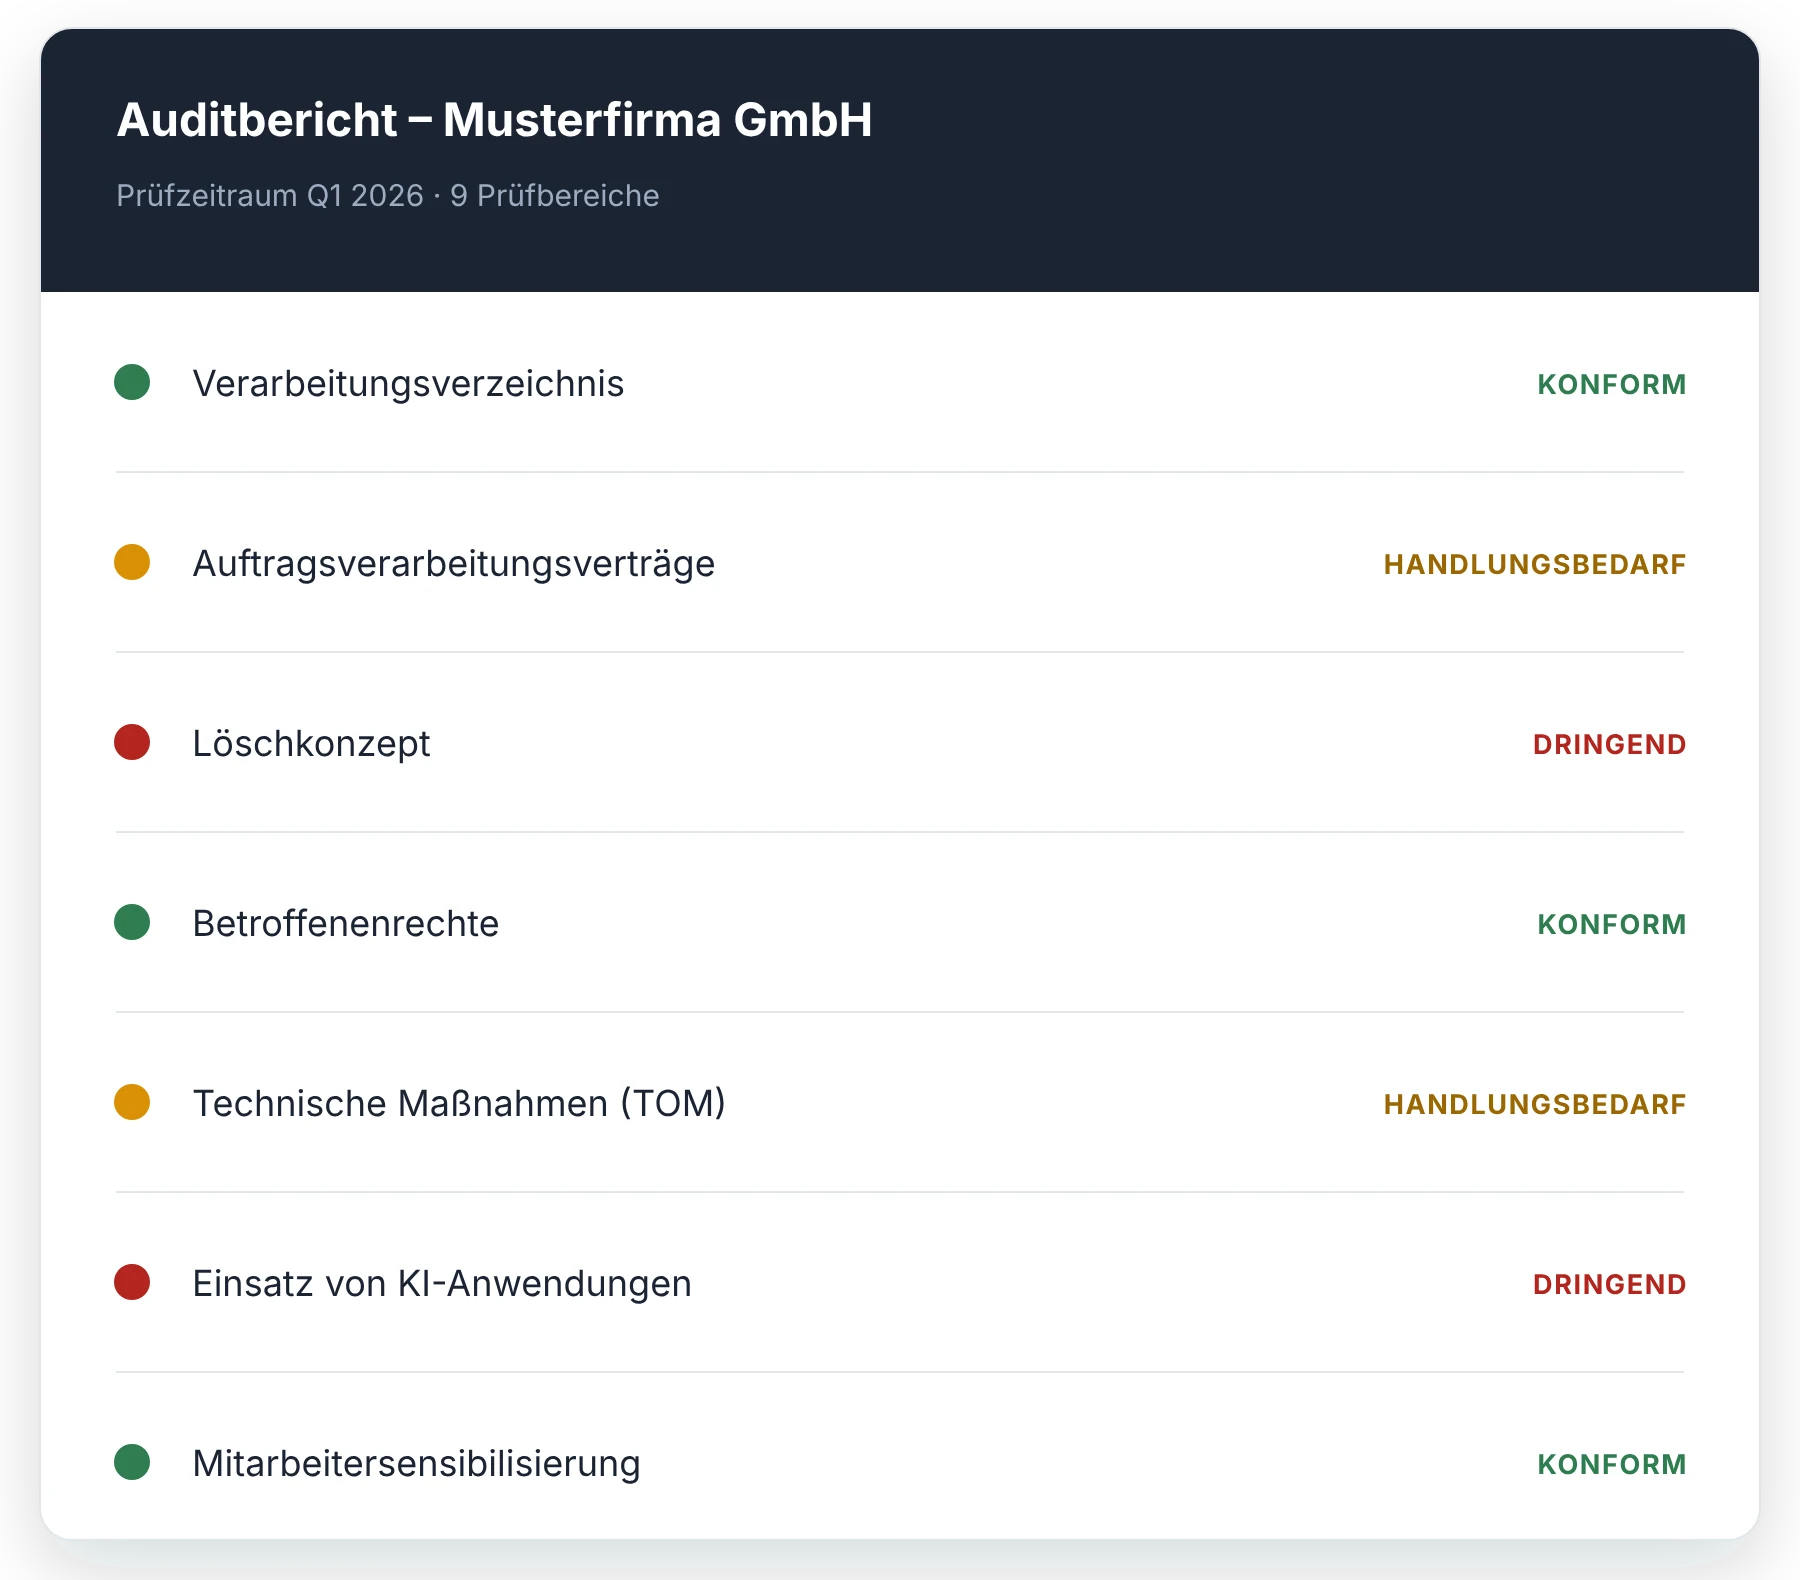
An audit is only worth something if it leads to action. That’s why ours doesn’t end with a description of the situation, but with a list that you can work through.
The process
Four steps – not a project marathon
The most common concern about an audit is not the result, but the expense. Therefore, we keep your share as small as possible.
Step 01
Analysis
We will jointly determine what is being reviewed, what the reason behind it is, and which areas are prioritized.
free of charge · approx. 45 min.
Step 02
Documents & Interviews
They provide existing documents; we speak with the responsible parties from IT, HR, and specialist departments. On-site or remotely.
about 4–6 hours of your time
Step 03
Analysis & Evaluation
We compare the current situation with the legal requirements and recommend concrete measures.
about 2 weeks
Step 04
Report & debrief
You will receive the audit report and we will go through it together. Including a recommendation on the order in which you can address the issues.
Closure
Who is checking
An audit is only as good as the people who carry it out.
Data protection is rarely just a legal issue. When it comes to deletion routines, log data, or AI systems, you need someone who understands the technology behind it. At us, both perspectives are in the same house.
Specializing in data protection for over two decades
Certified Data Protection Officers on the team
Disciplines under one roof: Data protection, law, information security, artificial intelligence and software development
What customers ask before the audit
How much does a data protection audit cost?
The price depends on the size of the piece. After the free initial consultation, you will receive a quote.
How much work is involved for us?
We take on most of the work. On your side, we need existing documents and around four to six hours for discussions with the responsible parties.
What happens if the audit finds serious deficiencies?
Then you have achieved exactly what an audit is intended to achieve. You decide what to implement in what order; if desired, we can accompany you in the process.
Is a data protection audit legally required?
An audit as such is not required. However, GDPR it includes various requirements for auditing and verification, in particular accountability and the review and, if necessary, updating of the measures taken. For the security of processing, Article 32(1)(d GDPR) explicitly requires a procedure for the regular review, assessment and evaluation of the effectiveness of technical and organizational measures. An audit can contribute to this, but is neither the most practical nor the legally prescribed way. If a data protection officer has been appointed, the monitoring of compliance with GDPR their statutory duties is also part of their responsibilities.
Do you also audit AI applications used internally?
Yes. The use of AI systems is now one of the most common checkpoints. – from customer service chatbots to assistance features in office software. We look at GDPR both the requirements and the obligations under the AI Act.
Clarity begins with a conversation
Non-binding · 15 minutes · Free
more SERVICES